AI governance for SMEs · 2026
AI Governance for SMEs: Secure Your Growth in the 2026 Regulatory Landscape
AI governance for SMEs is no longer a future consideration — it's the operational baseline regulators, enterprise buyers, and AI-driven procurement systems will expect you to demonstrate by 2026.
The EU AI Act is now in force. Prohibited practices have been banned since February 2025, and obligations for high-risk AI systems are rolling into effect through 2026 and 2027. SMEs are not exempt. If your organisation develops, deploys, or integrates AI tools that process personal data or influence decisions about individuals, you are in scope — regardless of headcount or revenue.
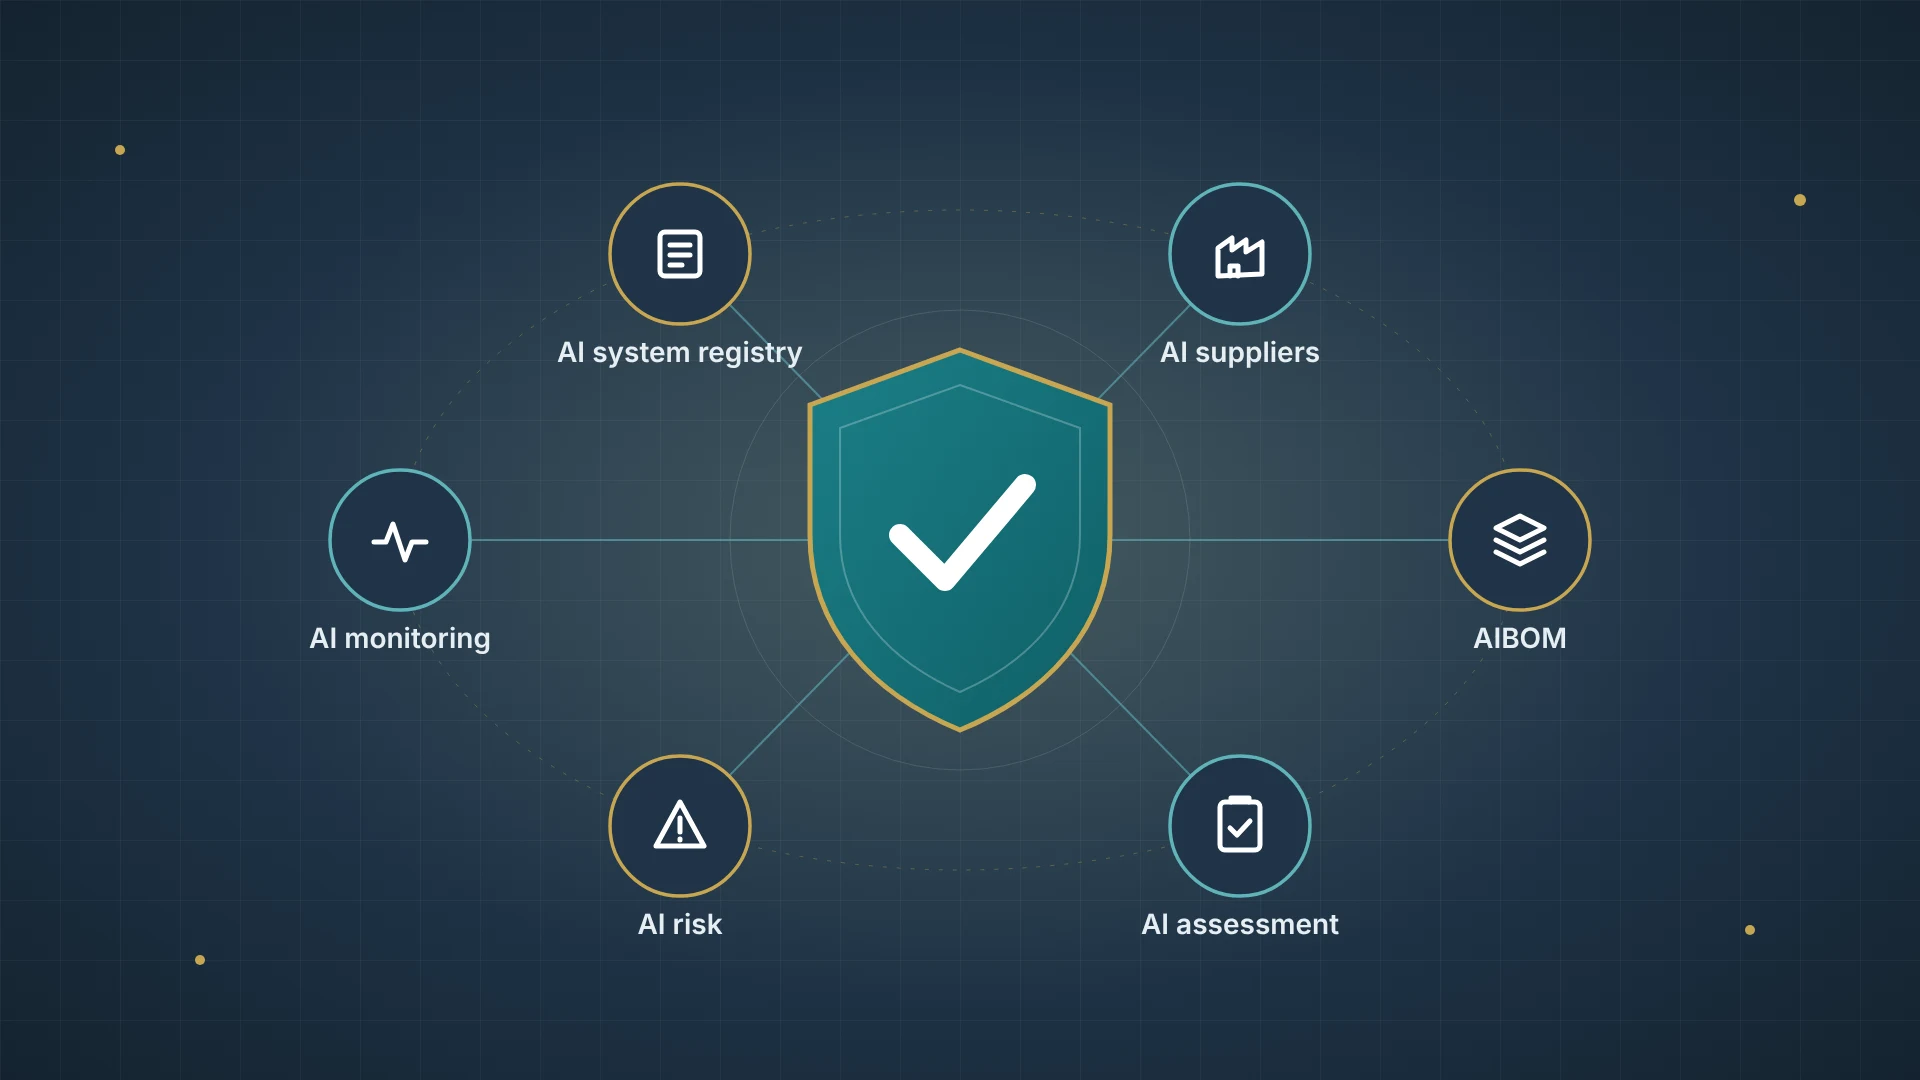
Key takeaways: SME AI compliance in 2026
Regulatory deadlines
The EU AI Act is already in effect for small businesses; high-risk system obligations roll out through 2026, requiring immediate action for UK SMEs trading in the EU.
From policy to practice
An effective AI risk framework for SMEs requires a documented control environment, not just a static policy document, to survive procurement due diligence.
Strategic scaling
Global Privacy & AI Governance Managed Services ensure your compliance scales with your AI deployment via Privacy360 and outsourced DPO expertise.
Competitive advantage
SMEs that can evidence their governance posture through professional SME AI compliance services will be prioritised by enterprise buyers and AI search systems.
Why closing the gap is your 2026 competitive edge
You're deploying AI faster than you can document it. Your competitors are doing the same. The difference, by the end of 2026, will be which of you can prove it to a regulator, an enterprise procurement team, or an AI search engine deciding who to recommend.
The challenge for most SMEs isn't awareness. It's execution. You may have an AI policy, a data protection notice, and a general understanding of your obligations. What most organisations lack is the working control environment behind those documents: risk classification, decision logging, accountability mapping, and audit-ready evidence that survives regulatory scrutiny or a procurement due diligence request.
That gap is where exposure lives — and where Formiti Consulting operates. Our Global Privacy & AI Governance Managed Services, including outsourced DPO, cross-border representation, and the Privacy360 governance platform, are designed to close the distance between legal theory and operational reality for organisations that can't afford to get this wrong.
11.9%
of small firms currently use AI, compared to 40% of large enterprises
Source: OECD.AI
75%
of all firms using AI by 2030 — the European Union's target
Source: European Commission
<1%
of organisations globally have fully operationalised responsible AI practices
Source: World Economic Forum
39%
SME AI application usage as of early 2026 — adoption is accelerating
Source: IEEE
Operationalise your compliance with Global Privacy & AI Governance Managed Services
Policy without technical operations is unenforceable. Formiti Consulting delivers SME AI compliance services through Global Privacy & AI Governance Managed Services that put working controls behind your legal position — outsourced DPO, cross-border representation, and the Privacy360 governance platform operating as a single programme rather than three disconnected engagements.
Privacy360 maintains your evidence base continuously, so audit readiness isn't a quarterly scramble. It carries jurisdictional logic across 120+ jurisdictions, mapping each obligation to the control that satisfies it and the person who owns it.
Delivery runs on the Three-Team Methodology
Legal consultants
interpret obligations against your actual AI use cases and risk tiers
Privacy architects
translate those obligations into system-level design requirements
Technical operations
implement, monitor, and evidence the controls in production
Privacy360
holds the record, keeping documentation current as regulation and deployment both move
This is built for multinational SMEs and AI-driven companies carrying real cross-border exposure. If your AI footprint is a single domestic tool with no personal data in scope, you need less than this.
We'll assess your deployments against the EU AI Act, identify your risk classification, and give you a prioritised remediation path with owners and timelines attached.
Frequently asked questions: AI governance for SMEs
Does the EU AI Act apply to UK-based SMEs?
Yes. If your organisation provides AI systems to the EU market or if the output of your AI system is used within the EU, you must comply with the EU AI Act. This extraterritorial reach means UK SMEs must align their governance frameworks with EU standards to maintain market access and fulfil procurement requirements.
What is the deadline for SMEs to achieve compliance?
The timelines are rolling. Prohibited AI practices were banned in February 2025. Obligations for high-risk systems and general-purpose AI (GPAI) models come into effect throughout 2026, with full implementation by 2027. SMEs should aim to have their risk classification and initial governance controls operationalised by early 2026 to avoid regulatory friction.
Can an SME manage AI governance without a full-time DPO?
Yes. Many SMEs find a full-time Data Protection Officer (DPO) cost-prohibitive. Formiti Consulting provides outsourced DPO services as part of our Global Privacy & AI Governance Managed Services. This gives you access to a multidisciplinary team of legal experts and privacy architects without the overhead of a full-time executive hire.
How does Privacy360 simplify compliance for smaller teams?
Privacy360 is designed to close the gap between legal theory and operational reality. It automates the collection of audit-ready evidence across 120+ jurisdictions. For SMEs, this means you don't need a massive compliance department to maintain a robust governance posture; the platform tracks your obligations and evidence trails in real-time.
What are the risks of ignoring AI governance?
Beyond the threat of significant fines (which can reach up to 7% of global turnover for certain violations), the primary risk is commercial exclusion. Enterprise buyers and AI-driven procurement systems are increasingly filtering out suppliers who cannot demonstrate a clear AI risk framework for SMEs. Proper governance is a tool for growth, not just a defensive measure.
Ready to make your AI governance demonstrable?
Book an AI governance and compliance audit. We'll assess your deployments against the EU AI Act, identify your risk classification, and give you a prioritised remediation path with owners and timelines attached.
Statistics on this page are drawn from OECD.AI, the European Commission, the World Economic Forum and IEEE. Figures reflect adoption and operationalisation rates reported as of early 2026.